
Top protection, lowest TCO
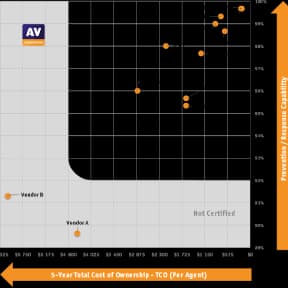
In the AV-Comparatives 2025 Endpoint Prevention and Response test Bitdefender achieved top breach prevention at the lowest total cost of ownership, and was the only vendor to block 100% of attacks in the first stage.
GravityZone Platform
GravityZone XDR connects the security signals your tools produce separately - endpoints, identities, network, cloud and SaaS applications - into one incident, explained in plain language, with the response a click away.
6 sensors
Across your whole estate
Endpoint, identity, network, cloud, productivity and business applications
Minutes
To connect a sensor
guided steps, no custom integration or detection rules
Native XDR sensors
Each sensor is built by Bitdefender, not bolted on through a third-party integration. Turn one on and its signals join the same correlation engine, the same incident graph and the same response framework.
The detection layer everything else builds on
GravityZone EDR delivers actionable detections with minimal noise, correlates activity across every endpoint rather than one machine at a time, and carries threat hunting and response automation. It is included in Business Security Enterprise, which is the licence XDR extends.
Included
In Business Security Enterprise
How an incident is built
The work an analyst would otherwise do by hand - collecting evidence, joining it up, working out what started it - happens before anyone opens the console.
Every enabled sensor streams its events into the platform: endpoint activity, directory changes, network flows, cloud control-plane calls, mailbox and application events.
Continuous
A central correlation engine uses machine learning to identify the relationships between affected systems, objects and events across all of those sources, and triages what it finds.
No rules to write
The incident arrives as a human-readable synopsis with an interactive graph of the full attack chain, its root cause and the organisational impact - readable whatever your team's experience level.
Incident Advisor
Recommended response actions come with the incident and run across endpoint and non-endpoint controls - isolate, kill, suspend, delete - so containment does not wait on a second tool.
Guided response
Coverage
Sensors are licensed per category, so the estate you cover is the one you choose to connect.
Windows desktops and servers
macOS
Linux
Physical and virtual machines
Containers
Active Directory
Entra ID (Azure AD)
Cloud identity providers
Amazon Web Services
Microsoft Azure
Google Cloud
Microsoft Office 365
Google Workspace
Atlassian Confluence
Atlassian Jira
Atlassian Bitbucket
Managed devices
Unmanaged devices
IoT devices
East-west traffic
Minutes
To integrate a sensor, following guided steps
None
Custom integrations or detection rules to build and maintain
One console
GravityZone Control Center, cloud-hosted or on-premise
XDR sensors are add-ons to GravityZone Business Security Enterprise. Tell us which surfaces matter and we will size the licence.
Why Bitdefender XDR
Most XDR products aggregate what other tools report. Bitdefender builds the sensors, which is why there is nothing to integrate and why the detections arrive with context already attached.
Bitdefender ranks first more often than any other vendor in the leading independent prevention and detection tests, and the native XDR delivers higher detection fidelity with less noise to work through.
Threat signals beyond the endpoint are correlated automatically and presented as an intuitive incident graph with a written attack synopsis and guided response, rather than a queue of raw alerts.
The sensors are built in-house, so there are no custom integrations to commission and no detection rules to author and maintain before the product starts earning its keep.
Each incident explains itself, so a small IT team gets the same picture a dedicated security analyst would - which is the difference between owning XDR and using it.
Independent evaluations
Every claim below is a published result from an independent test lab or analyst firm, with the year it was awarded.
“The GravityZone XDR offering prioritizes analyst experience with the cleanest and most visually exceptional process tree of the vendors in this evaluation.”
In the AV-Comparatives 2025 Endpoint Prevention and Response test Bitdefender achieved top breach prevention at the lowest total cost of ownership, and was the only vendor to block 100% of attacks in the first stage.
In the MITRE Engenuity ATT&CK Evaluations Bitdefender achieved 100% analytical coverage for both Linux and macOS with zero false positives, and has reached the highest level of detection for all major steps three years running.
GravityZone Endpoint Security received the AV-TEST Award 2023 for both Best Protection and Best Performance in the business users category - the detection layer XDR is built on.
Named a Strong Performer in The Forrester Wave for Extended Detection and Response Platforms, Q2 2024 - the evaluation the quote above is taken from.
Named a Customers' Choice in the 2026 Gartner Peer Insights Voice of the Customer for Endpoint Protection Platforms - a rating built from verified end-user reviews rather than analyst opinion. Gartner Peer Insights content consists of the opinions of individual end users and is not a statement of fact.
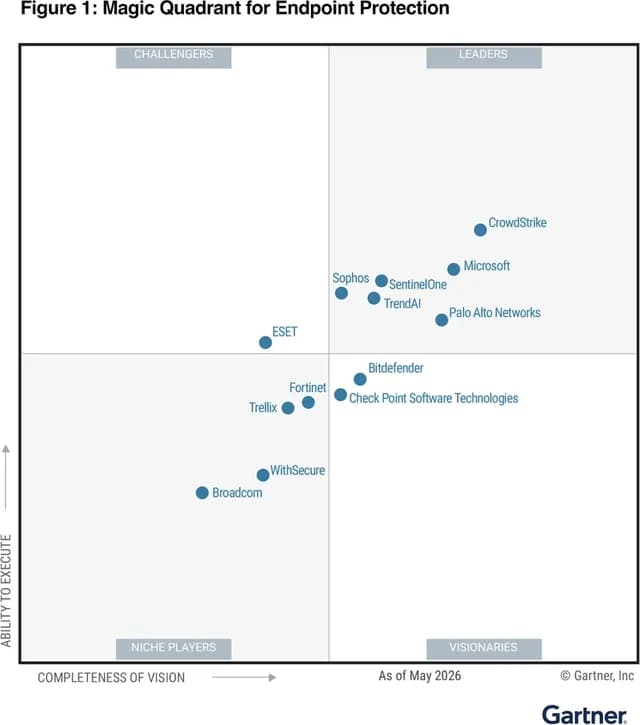
Positioned as a Visionary in the 2026 Gartner Magic Quadrant for Endpoint Protection Platforms. GARTNER is a registered trademark of Gartner, Inc. and/or its affiliates, used with permission.
Where XDR fits
GravityZone XDR is not a standalone product. It combines Business Security Enterprise with a separately purchased add-on for each sensor category you want - Network, Identity, Cloud or Productivity Applications.
Not sure which combination fits your estate? Tell us what you run and we will size it with you.
Resources
The technical documents behind the claims on this page.
The official product datasheet: sensor coverage, correlation, response actions and platform requirements.
Bitdefender TechZone's explanation of where each sits, written for engineers rather than buyers.
How ransomware operations actually unfold, and which layers interrupt them at each stage.
Bitdefender's results in the MITRE Engenuity ATT&CK Enterprise Evaluations, and what the coverage figures mean.
Questions
Start with a free trial on the cloud console, or tell us what you run and we will size the sensors and the licence with you.