Cross-Endpoint Correlation
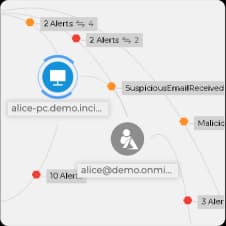
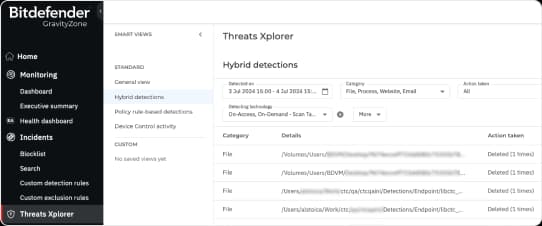
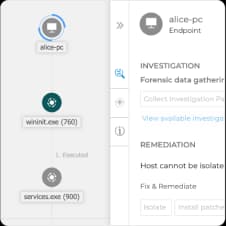
Most tools raise an alert per machine and leave an analyst to work out that the alerts are the same attack. GravityZone EDR does that automatically: related detections on separate endpoints are consolidated into one larger incident, so the estate-wide shape of an attack shows up as a single item to work. Bitdefender states this is the only EDR on the market that correlates attacks across endpoints automatically.
- Detections on separate machines are consolidated into one incident
- Response actions are offered on the node you select in the graph
- Forensic data gathering, host isolation and remediation from the same view